
ISO/IEC 27001:2022 · Information Security Management System Consulting
Not just a certificate — a team that builds real security.
We help you build an ISMS that remains effective after the certification audit. Our service combines TSE Class A penetration testing, KVKK compliance, online awareness training, and social engineering exercises under one contract. We implement the applicable Annex A controls and document the evidence in your Statement of Applicability (SoA).
- TSE Class A Penetration Testing
- CREST Member
- 400+ Corporate References
- 25 Certified Experts
01 — Success Stories
Three Major Organizations, Three Different Sectors
From exam security to banking, logistics to public service — same discipline, same team.

ÖSYM
An information security awareness program for exam security and candidate data protection, run in separate modules for staff, proctors, and technical teams.
Read more
Türkiye İş Bankası — İşmer
An ISMS control environment integrated with BDDK and KVKK. Annex A 5 (organizational) and Annex A 8 (technological) controls aligned with banking operational requirements.
Read more
Kolay Gelsin
A multi-site ISMS program covering head office, data center, and field operations for a delivery infrastructure reaching millions; passed the accredited audit successfully.
Full success story02 — Annex A Technical Implementation Team
We Don't Just Write It in the SoA — We Build It
Competing consultants tick the Annex A item in the Statement of Applicability and leave the rest to the client's IT. We implement Annex A technological controls in the field with our technology partners.
Annex A 8 — Implementation Support for Technological Controls
For technical controls marked in the SoA, product procurement, architecture design, and implementation proceed together.
03 — Included in Your Service
Far More Than an ISMS Certificate
Our service scope goes beyond the ISO 27001 clauses.
ISMS Implementation and Documentation
40+ policies, procedures, forms, and all mandatory records including the SoA.
Online Awareness Training Platform
Training for all staff via the Nesil Online Training Platform, with participation and performance reports.
Social Engineering Simulation Platform
Phishing exercises with the Nesil Social Engineering Platform; resilience measurement.
Penetration Testing TSE Class A
Field evidence for Annex A 8.8 (management of technical vulnerabilities); web, network, and AD testing.
KVKK Compliance Integration
ISMS and KVKK Article 12 technical measures in a single control environment.
Risk Assessment and Internal Audit
ISO/IEC 27005 methodology; internal auditor training and the first audit.
Pre-Certification Mock Audit
Gap identification and closure before the accredited certification body audit.
Post-Certification Support
ISMS sustainability across the three-year surveillance audit cycle.
04 — Platforms We Built
We Back Consulting with Software
We deliver working systems, not PDFs.
Nesil Online Training Platform
PlatformISMS awareness training modules, per-employee tracking, performance reports. Infrastructure field-tested with 3,000+ users at ÖSYM.
Nesil Social Engineering Platform
PlatformSocial engineering exercises, post-training retests, resilience reports. Awareness evidence for ISO 27001 Annex A 6.3 and KVKK Article 12.
05 — The Team Behind the Service
The Same Team Builds the ISMS, Runs the Tests, Delivers the Training
Certified experts in the field, not automated reports. Lawyer, auditor, pentester, and systems engineer under one roof. Meet the full team →

Murat Kaya
ISMS Project Lead · ISO 27001 Lead Auditor
CISA · CISSP · ISO 27001 LA
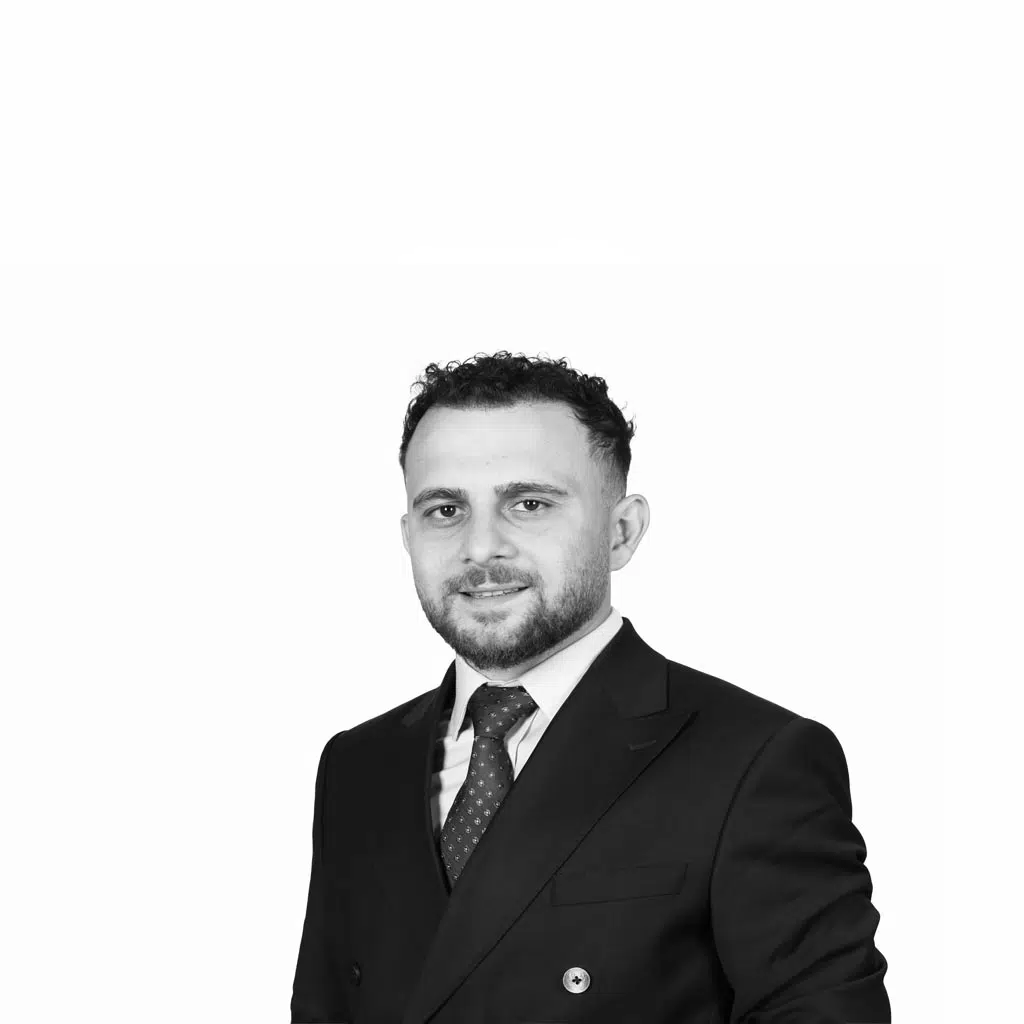
Uygar Yasin Aydın
Lead Auditor · Practice Lead
27001 LA · 27701 LA · CIPP/E · CISM

Atty. İrem Genç
KVKK Attorney · Ankara Bar Association
KVKK Specialist · Data Privacy Law

Atty. Rabia Dağcı
GDPR Attorney · Istanbul Bar Association
CIPP/E · DPA / SCC
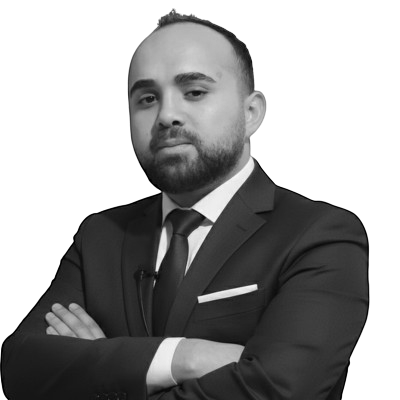
Alpaslan Aydın
TSE Senior Pentest Expert
OSCP+ · OSCP · CEH · LPT

Faruk Keten
Senior Systems Engineer · Infrastructure Hardening
MCSE · CCNA · Sophos

Enes Yüksel
Penetration Tester · Web · API · Red Team
OSCP · CEH · eWPTX
06 — Introduction Deck
Detailed Introduction Document
Review our introduction deck covering our approach, 12-step methodology, and KVKK mapping tables.
ISO 27001 ISMS Introduction Deck
Download the Deck07 — About ISO 27001 Consulting
What to Know When Choosing an ISO 27001 Consultant
ISO 27001 consulting is the professional service that helps organizations build and operate an information security management system (ISMS) to ISO/IEC 27001:2022 requirements and prepare for the accredited certification audit. The right ISO 27001 consultant does more than draft policies and procedures: they analyze the organization's processes, map its risks, implement Annex A controls in line with field reality, and run internal audit and management review hands-on.
At Nesil Teknoloji, the critical difference that separates our ISMS consulting from other ISO 27001 consulting firms is that we offer penetration testing, KVKK compliance, online awareness training, and social engineering simulation under a single contract. TSE Class A penetration testing certification (TS 13638/T2, No. TSE-STF-065) and CREST membership let us produce field evidence for Annex A 8.8 (management of technical vulnerabilities) with our own team. With KVKK attorneys registered with the Ankara and Istanbul Bar Associations, we manage KVKK Article 12 technical measures within the same control environment as ISO 27001.
Related regulations and standards: ISO 27701 PIMS (Privacy Information Management System), ISO 42001 AI Management System, NIST SP 800 and DORA integrated implementations. For ISMS maturity assessment, see our regulation-compliant penetration tests.
Where We Deliver ISO 27001 Consulting
We deliver ISO 27001 consulting across Türkiye from our Ankara and Istanbul offices. We have run field engagements in: Ankara, Istanbul, İzmir, Bursa, Antalya, Kocaeli, Konya, Adana, Gaziantep, Kayseri, Mersin, Eskişehir, Samsun, Trabzon, Diyarbakır. For multi-site organizations we design ISMS programs covering head offices, branches, production facilities, and distribution centers. For clients with international subsidiaries, we also bring GDPR-integrated ISO 27701 PIMS implementations into scope.
Which Industries Do We Serve?
Industries using our ISMS consulting: finance (BDDK compliance), insurance, capital markets (SPK), energy, government, defense, healthcare, logistics and distribution, e-commerce, software and technology, manufacturing, telecommunications, and education. Sector regulation integration (BDDK, SPK, EPDK, TCMB, MASAK, Law No. 5651) is managed as a single compliance environment within the ISMS control set.
What Drives ISO 27001 Consulting Cost?
The main cost drivers: headcount, number of locations, business processes in scope, IT infrastructure complexity, current maturity level, and sector regulation needs. A typical project takes 4–6 months for a mid-size SME and 8–12 months for large enterprises. For a tailored proposal, complete our scoping form (Turkish) or call +90 850 532 08 96.
08 — Frequently Asked Questions
Questions About the Process
How long does an ISO 27001 ISMS consulting engagement take?
4–6 months for a mid-size SME; multi-site and complex IT environments can take 8–12 months. The minimum duration is driven by the need to produce internal audit and management review evidence.
Do you guarantee ISO 27001 certification?
Certification authority belongs to accredited certification bodies — not to consultants. When the ISMS is built to the standard and internal audit and management review are complete, the likelihood of passing the certification audit is at its highest.
Must internal audits be done by an external firm?
ISO/IEC 27001 Clause 9.2 requires internal audits to be independent and impartial — that doesn't mean an external firm is mandatory. Trained in-house internal auditors satisfy the requirement. Within our consulting, we build the internal audit team and run the first audits together.
Is ISO 27001 only an IT department matter?
An ISMS covers people, process, and technology in full. HR, Procurement, Legal, Administrative Affairs, Operations, and executive management take on roles and responsibilities from Clause 5 onward. IT is only one of the components.
Is consulting needed after certification?
Certification runs on a three-year cycle: the initial audit, two years of surveillance audits, and recertification in year three. Sustainability consulting is the common choice for keeping the ISMS alive across that cycle.
What does Nesil Teknoloji do differently in ISO 27001 consulting?
A single contract covers ISO 27001 consulting, TSE Class A penetration testing (TS 13638/T2), KVKK compliance (with Ankara and Istanbul Bar attorneys), awareness training via the Nesil Online Training Platform, and phishing simulation via the Nesil Social Engineering Platform. Field implementation of Annex A technological controls is in scope too.
Meet the ISMS Team — Murat Kaya
ISO 27001 ISMS consulting Let's define the scope together. In a 30-minute online meeting we discuss organizational context, ISMS boundaries, the roadmap, and delivery process — then share our proposal.
- Preliminary discovery and ISMS scope validation (specific to your organization)
- ISO/IEC 27001:2022 aligned roadmap and timeline
- Fast quoting and start date
Send the completed form to [email protected] or call: 0850 532 08 96 · Serving all of Türkiye from our Ankara and Istanbul offices.